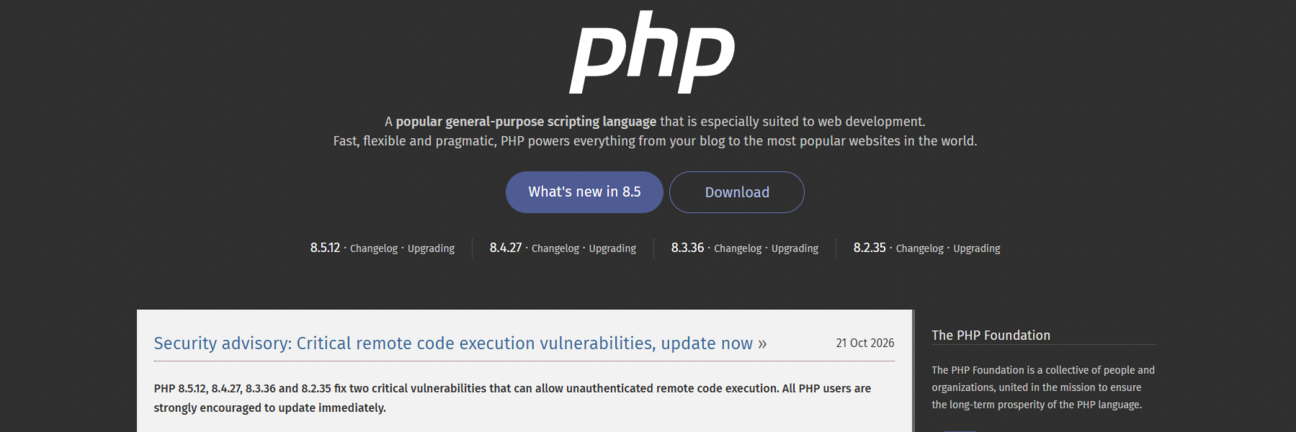
PHP vulnerabilities mitigated and patched within 22 minutes
As you'll have seen in the news, there was a major cyber-security alert yesterday (21st October) https://www.bbc.co.uk/news/articles/cmly0lg3w5x2o
It became clear that vulnerabilities in PHP (a service that supports around 70% of website worldwide) had been discovered and publicised hours before the fix for those vulnerabilities was released.
When the news broke, Prater Raines put a number of mitigations in place based on the limited information that was publicly available at the time. These included disabling various admin areas and preventing form submissions from mid-morning. We then prepared and watched for the patch release, and installed the patched version of PHP immediately it was released (2.36pm BST).
As of 2:58pm on Wednesday 21st October our web servers were therefore no longer at risk. We're proud to say this was just 22 minutes after the initial public release of the patched PHP source code, and 2 minutes before its scheduled release! It was also rather before the news story even got the the front page of the BBC news website (in fairness to the BBC, it was in their tech section for a couple of hours before).
Like every other web host using PHP today, we're still checking our systems for any attempt to test for or exploit the vulnerability before it was patched. We've found none, and there has, as yet, been no evidence of the vulnerability being exploited although there was considerable evidence of attempts to exploit it before the patch was released.
It's action like that we charge a hosting support fee is for: it's important that our service includes regularly keeping your software up to date. Those hosting their sites with an out of date version of PHP today: good luck.